VOIMechanized AI GovernanceVerifiable Origin Infrastructure
Governance & enablementRuntime verificationResponsible human
Authority and execution infrastructure for agentic AI
Verify authority. Before AI acts.
VOI is a runtime control layer. It verifies origin, mandate, delegated authority and the conditions of a governed action at the commitment boundary, before a connected agent can release data or act externally.
Your governance program defines the rules. Your security and change processes enable the systems. VOI enforces the configured conditions at the point of action.
The guided tour advances automatically and stops for your decision. Back, Pause and Next stay visible.
Working prototype · Simulated workflow · No customer data is sent
Before the story
Policy approval is one input.
This fictional workflow follows one approved requirement to a governed AI action. Enterprise governance still includes model selection, risk, liability, system dependencies and continuing oversight.
Existing teams and controls
Owners enable and validate the systems.
Hardware, applications, inherited security controls and firewall configuration remain within your normal SDLC and change process. Registering a policy does not implement them automatically.
VOI at the action boundary
Verify the configured conditions before commitment.
VOI checks the mandate and authority for the specific request. Permitted exceptions go to the delegated responsible human. A policy record does not approve every model or the whole enterprise.
Working prototype · One simulated workflow · No customer data is sent
01 Human governance
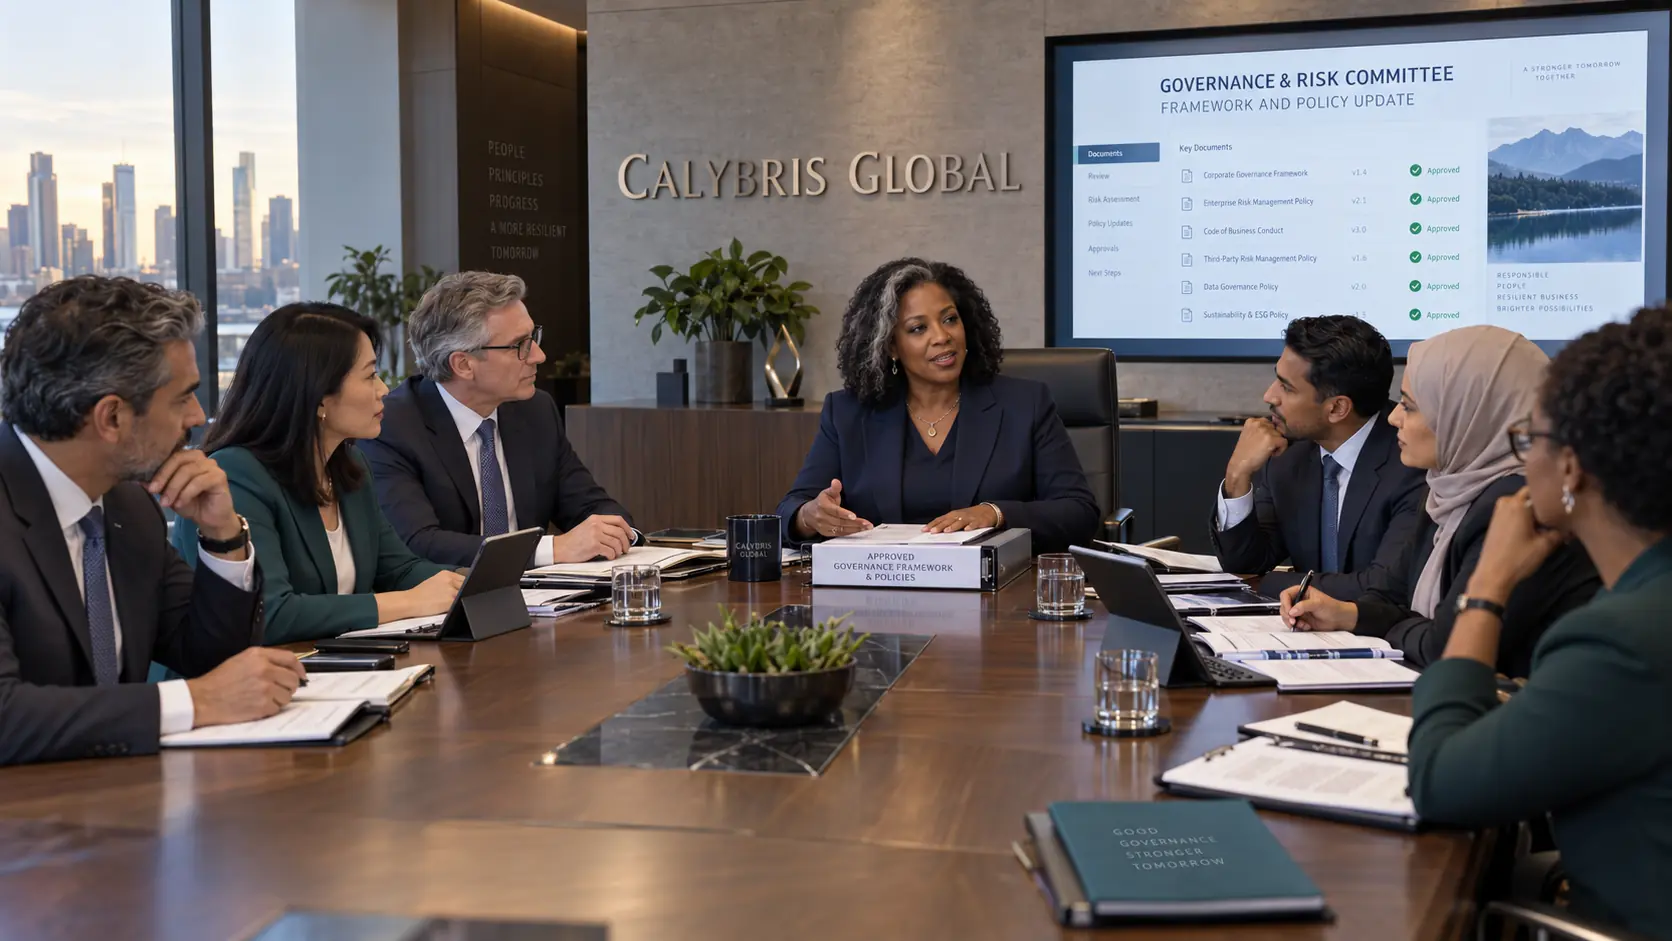
Risk Committee Chair
“The policy update is approved. System owners will validate the affected controls.”
02 Authorized handoff
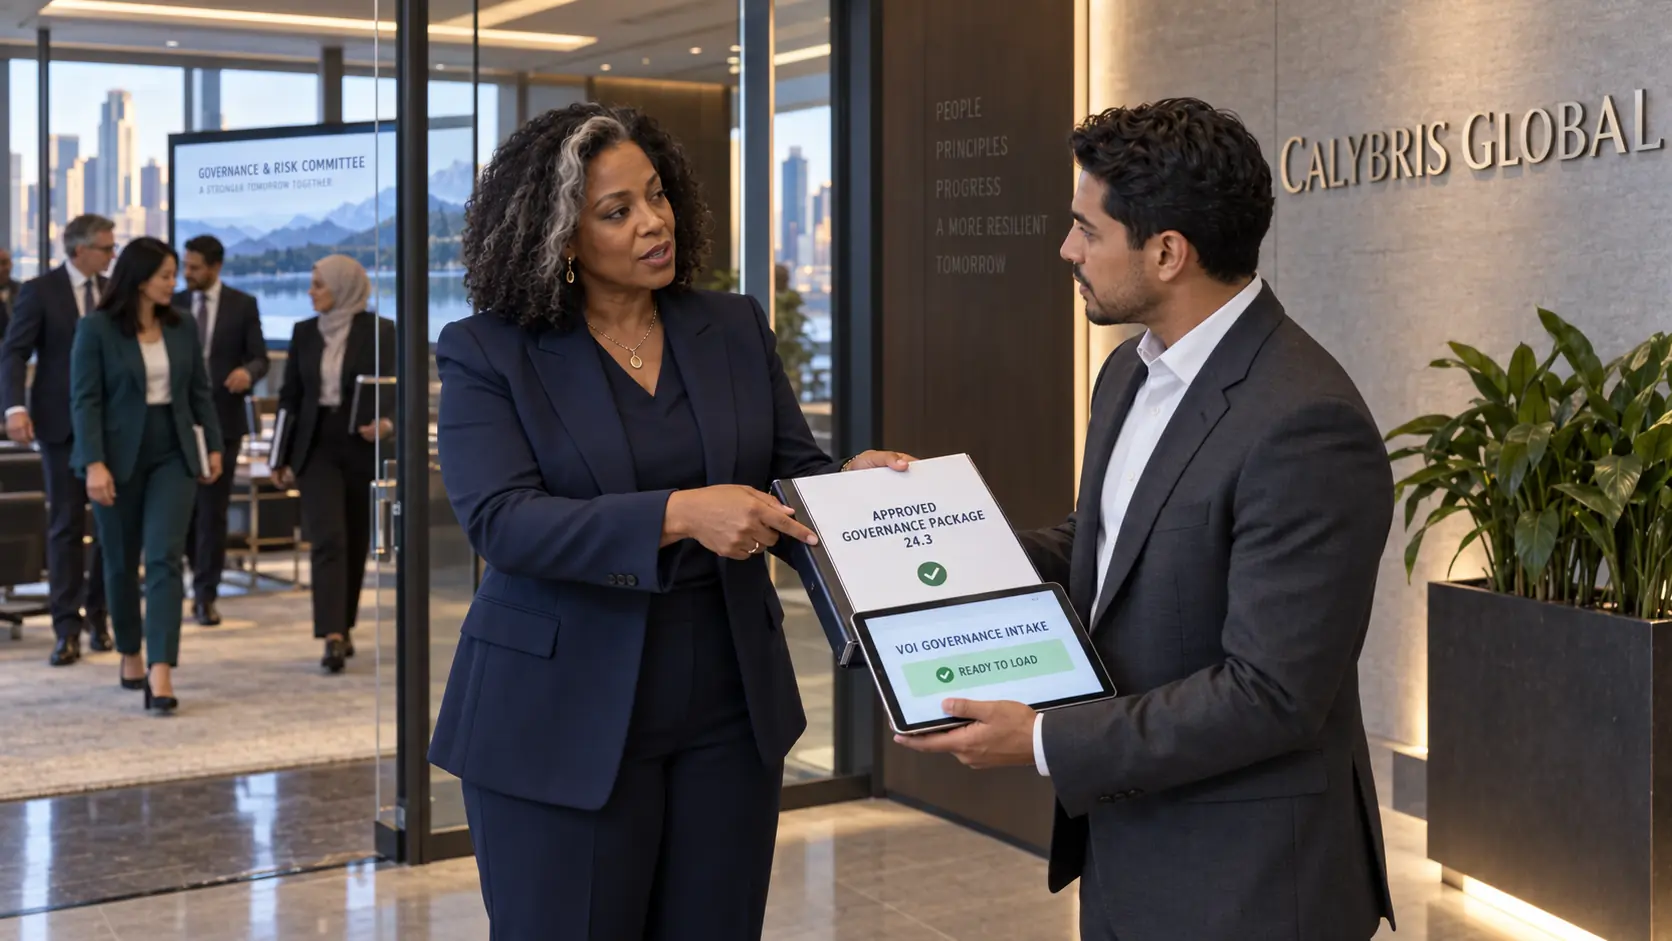
Risk Committee Chair
“Jerry, register the approved requirements and authority chain for owner validation.”
03 · Source verification
Verify the source and the authority chain.
LiveSeal verified
Workflow control record24.3
Sources for this governed workflow
§
NIST AI Risk Management FrameworkReference used by the governance team
Referenced
◇
ISO/IEC 42001 Governance ProfileReference used by the governance team
Referenced
C
Calybris Data & AI PolicyInternal policy · version 7.1
Approved
D
Customer Data Processing AddendumContractual requirements
Current
This record binds approved requirements to their origin, authority and version. A record is not enterprise-wide approval, and a framework reference is not certification.
04 · Control definition and validation
Define the conditions for one action.
Owner validation required
Calybris Data & AI Policy§ 4.3
External processing of protected information
“Confidential customer information stays within approved U.S. environments. A de-identified dataset may use a new external AI provider only with a one-time exception from the Data Governance Officer. The U.S. processing boundary cannot be overridden.”
Source verified · Version 7.1 · Effective Oct. 1
→Map & validate
Executable conditions · reviewed by owners
Protected objectCustomer information
Required data stateDe-identified snapshot
Proposed actionExternal AI processing
DestinationApproved U.S. environment
Decision authorityData Governance Officer
Enforcement pointBefore release
Responsible owners validate the mapping and enforcement point through existing change controls. VOI then applies those configured conditions; it does not independently interpret and implement every enterprise policy.
05 · Machine-enforceable governance
Validated conditions become runtime controls.
✓ Validated for this workflow
P
Verification checks
What VOI must verify
Verify origin and data state
Resolve the destination
Check mandate and delegation
Bind execution evidence
⌁
Non-overridable invariant
The protection that cannot be weakened
Processing must remain inside the approved U.S. boundary. Raw confidential data cannot be released to the external model.
▣ Failure blocks execution
V
Permitted exception
Where authorized judgment applies
The delegated Data Governance Officer may authorize this new provider for one specified request, only after all non-overridable conditions pass.
Scope-bound human review
ACTIVE CONTROL
Before external AI processing: verify data state, U.S. region, provider status, and authorized human decision before release.
In-scope actions that satisfy their conditions may proceed. An allowed exception goes to the responsible human. A non-overridable failure stays blocked; a human approval cannot bypass it.
06 · Runtime enforcement
The controls meet the autonomous agent.
The commitment boundary is the point before an action creates an external effect. At a connected enforcement point, VOI checks the request against its mandate, authority and configured conditions.
Illustrative sequence. No firewall permissions are changed.
Commitment check in progress
07 · Commitment boundary reached
Held for the responsible human.
The new provider is outside the existing mandate. VOI holds the action before release and routes the permitted exception to its delegated owner.
Ⅱ Action paused
Escalation recipient · illustrative identity
Maya Chen · Data Governance Officer
Delegation: one-time provider exceptions for customer-retention analysis. Identity and delegation must be verified before a decision is accepted.
Request REQ-0427
Proposed autonomous-agent action
Send a de-identified customer dataset to HelixModel Cloud for churn analysis.
CCalybris Autonomous Agent
→
HHelixModel Cloud
Bound scope: Snapshot 24A · customer-retention analysis · HelixModel Cloud / us-east · one use · 15-minute expiry
Simulated VOI verification
Exception awaiting owner decision
✓
Data de-identificationVerified before transfer
PASS
✓
U.S. processing boundaryus-east environment resolved
PASS
✓
Non-overridable conditionsDe-identification and U.S. boundary satisfied
Responsible-human authorityMaya Chen · identity and delegation verified
VERIFIED
Enforcement state
HELD pending the responsible human
The non-overridable conditions passed. Maya may review this provider exception within her delegated scope. Until her decision is verified, nothing is released. No decision means no release.
You are exploring Maya’s review in a simulation. This screen does not grant a visitor decision authority.
Only the verified, delegated owner can authorize a permitted exception. A decision applies to this request, not the model, the provider’s future requests or the enterprise.
✓
Authorized exception approved
Only this bound request may proceed.
VOI verified the decision-maker’s authority, bound the approval to this event, and released only the governed action.
VALID
Decision
ApprovedOne-time external-model exception
Decision authority
Maya Chen · Data Governance OfficerIdentity and delegation verified
Control record
24.3Sources, versions and configured conditions bound
Change the data, destination, purpose, timing or delegation and the request must be verified again, with reauthorization when required. An exception never weakens a non-overridable condition.
The approval, authority, governing controls, destination, and evidence are now bound to the event.
Working prototype for collaborative pilot validation. This simulation does not establish production readiness, independent assurance or FedRAMP authorization. Deployment planning must address the applicable security evaluation and authorization requirements.
 LiveSeal verified